Interface Contracts
Define allowed event sequences and interaction rules between components.
Model concurrent control behaviour explicitly, verify interface and component interactions before software integration, explore counterexamples and generate implementation artefacts from the verified design.
Capabilities and terminology aligned to the current partner portfolio and target application.
Define allowed event sequences and interaction rules between components.
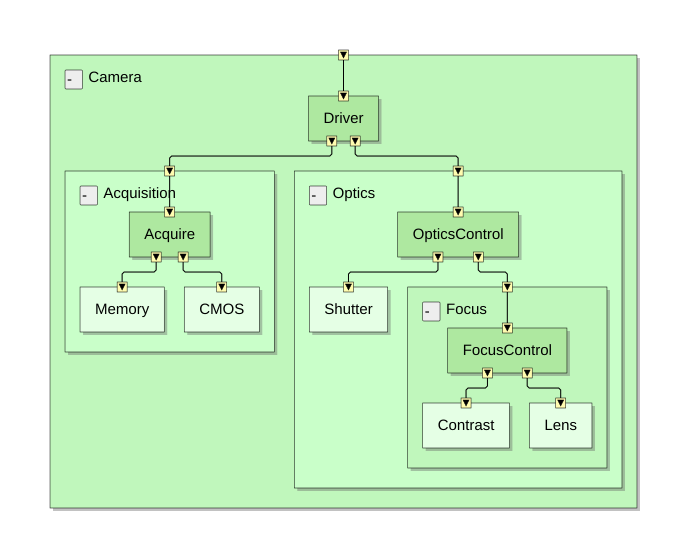
Represent state, behaviour and concurrency explicitly in the Dezyne language.
Check supported behavioural properties over the model state space.
Inspect traces that explain deadlocks, contract violations or other discovered defects.
Use state, sequence and system views to understand architecture and behaviour.
Generate C, C++ or C# artefacts for integration into the target application.
Relevant standards, coding guidelines and assurance frameworks for the technology and its application areas.
Industry connections are included where the technology addresses a defined engineering, verification or product-security requirement.
Connect the technology with the existing engineering environment, lifecycle tools, CI/CD platform and target architecture.
Dezyne language, LSP and graphical tools
Batch-mode verification for CI/CD
Generated source code with surrounding application and platform software